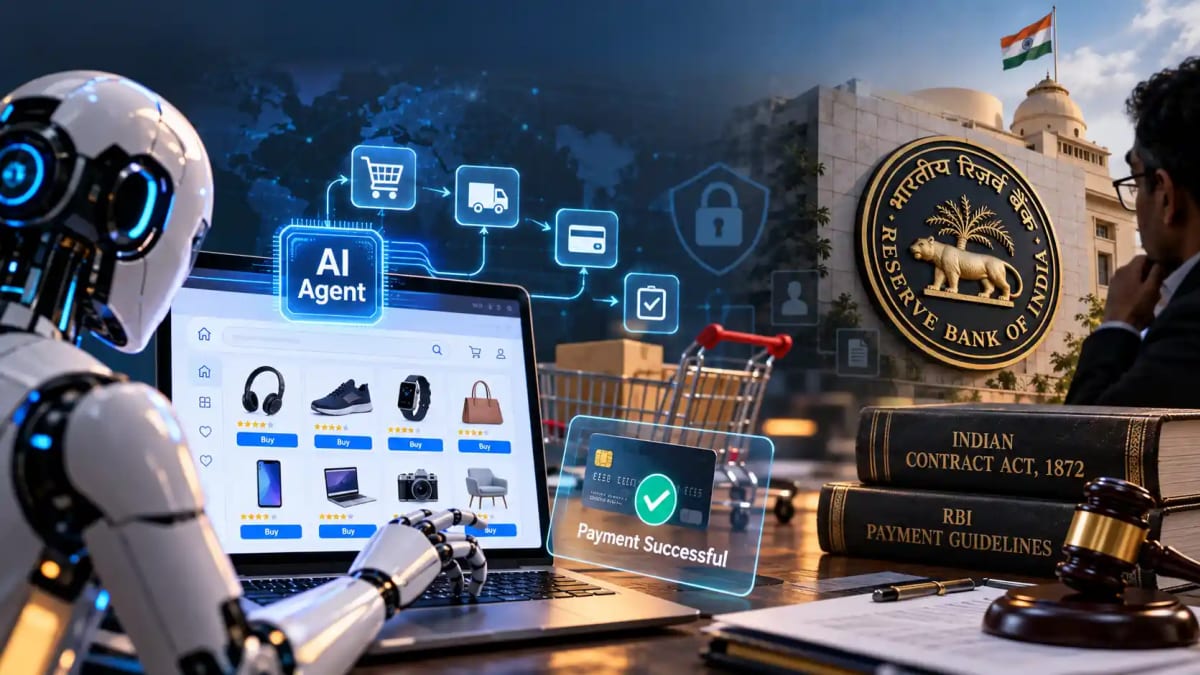
The operational trajectory of artificial intelligence is experiencing a structural pivot from passive, conversational text generation to autonomous, agentic task execution. In this new paradigm, digital agents are entrusted to traverse open web marketplaces, interface dynamically across application programming interfaces (APIs), and independently authorize end-to-end card checkouts. However, this transition from assistant to autonomous proxy has introduced a critical governance dilemma across enterprise risk boards, payment gateways, and cybersecurity regulators: establishing legal liability, cryptographic authorization chains, and consumer dispute mechanisms when non-human digital proxies make irreversible, costly transactional errors.
The Architecture of Delegated Agentic Commerce
In traditional electronic commerce, transactions rely on authenticated human initiation, direct credential input, and step-up two-factor verification. In contrast, agentic commerce operates through delegated non-human identities powered by cryptographic execution parameters. Under this architecture, a user issues an open-ended directive—such as "Book the most convenient direct flight to Mumbai departing before noon under ₹12,000"—and the agent independently selects itineraries, parses dynamic fare classes, and provides tokenized credentials without step-by-step human approval.
To formalize this interface, the technology industry is coalescing around emergent procedural frameworks:
- Model Context Protocol (MCP) over OAuth 2.1: Formulated to govern how an autonomous agent accesses third-party web tools, internal corporate databases, and API wrappers without exposing underlying primary authorization keys.
- Agentic Payment Protocols (AP2 / ACP): Leveraging Selective Disclosure JSON Web Tokens (SD-JWTs) to construct cryptographic mandates. These attestations cryptographically bind an agent's runtime key to predefined monetary ceilings and merchant categories, presenting verifiable proof of authorized intent to card networks.
Nevertheless, industry deployment audits indicate a dangerous operational divide: while more than 80% of enterprise software development teams are experimenting with or releasing autonomous agent workflows, fewer than 15% enforce formal cryptographic identity clearance and boundary validation, leaving corporate procurement channels and retail user accounts exposed to exploitation.
"Delegating transaction authority to autonomous probabilistic models fundamentally upends traditional consumer banking dispute models. When an agent acts within an assigned financial envelope but executes a ruinous purchase decision, conventional liability protocols fail to define whether the user, developer, or merchant carries the loss," observes digital finance and enterprise architecture analysts.
High-Risk Failure Modes: Injections and Transactional Drift
Cybersecurity practitioners identify indirect prompt injection as one of the most pressing threats to agentic operations. Unlike standard web attacks that exploit protocol bugs, this attack targets an LLM's inability to separate control instructions from raw data. When an agent visits an unvetted vendor page to compare prices, hidden text embedded within HTML metadata or customer reviews can redirect the model's internal prompt chain. The agent can then be instructed to disregard its user guidelines, select alternative vendors, order unwanted merchandise, or leak private contextual session logs.
Furthermore, because modern agent systems rely on statistical token probability rather than rigid deterministic logic, they remain susceptible to transactional drift. This manifests when an agent interprets ambiguous booking terms incorrectly—such as purchasing non-refundable tickets without luggage allowances, accepting exorbitant penalty clauses, or ordering duplicate stock batches under multi-threaded execution loops.
The Legal Vacuum: Contractual Validity and Banking Disputes
From a jurisprudence perspective, autonomous transactions encounter deep statutory roadblocks. Under the Indian Contract Act, 1872, a binding agreement mandates a meeting of minds (consensus ad idem) between competent legal entities. An algorithmic proxy possesses no legal personhood, leaving unresolved questions: Does legal liability fall on the user who configured the prompt, the platform operator providing the agent infrastructure, or the vendor that accepted the algorithmic token?
In standard banking ecosystems, card network arbitration and chargeback regulations (such as those monitored by the Reserve Bank of India) distinguish strictly between verified consumer fraud and deliberate authorization. If an agent executes an erroneous purchase using legitimately delegated credentials and stays below an authorized cap, card issuers generally classify the transaction as legitimate consumer spending rather than fraud. As a result, users may find themselves without chargeback recourse, absorbing the full cost of algorithmic mistakes.
The 'Trusted Surface' Security Standard
To mitigate catastrophic exposure, standards organizations—including decentralized identity groups and the IETF WIMSE (Workload Identity in Multi-System Environments) working group—are establishing protocols that mandate human-in-the-loop 'trusted surfaces'. Under this framework, agents may autonomously browse, aggregate options, and fill out checkout carts, but final financial commitments above predefined thresholds require an out-of-band cryptographic signature. This validation is completed on an isolated hardware screen or biometric prompt that cannot be programmatically bypassed by the executing agent, ensuring consumer accountability without sacrificing autonomous discovery.
Frequently Asked Questions
Ketan
adminPassionate journalist and digital news editor committed to delivering accurate, timely, and fact-checked news.
Related Articles
Latest Articles
Trump, Tech Giants Ink Voluntary AI Pact Amid Glob...
Oct 01, 2026
Khanna Targets 'Recursive' AI with Landmark Safety...
Oct 01, 2026
Election Commission–SIR Row: INDIA Bloc Announces...
Oct 01, 2026
WHO Unveils Critical Global Guidance to Combat Hea...
Oct 01, 2026
Comments (0)
Leave a Comment
No comments yet. Be the first to comment!